Subnetting Cheat Sheet: CIDR Mental Math, AWS Reserved IPs and an Interactive Speed Game
If you have ever prepared for a senior DevOps interview, an AWS Solutions Architect exam, or a CKA (Certified Kubernetes Administrator) certification, you have likely encountered this dreaded whiteboard scenario:
"You are provisioning a new VPC with 10.0.0.0/22. Carve out subnets for Web, Application, and Database tiers across 3 Availability Zones without overlapping CIDRs. What are the subnet masks, broadcast addresses, and total usable IP ranges per tier?"
For many engineers and junior cloud practitioners, subnetting feels like an archaic ritual from 1995 that we only tolerate because ipcalc and web calculators exist. Many assume that in a world of automated Terraform modules and managed cloud infrastructure, mental subnetting is an obsolete skill.
They could not be more wrong.
In enterprise cloud architecture, misunderstanding CIDR blocks is the leading cause of non-routable Transit Gateway topologies, broken VPC peering connections, and catastrophic production outages caused by Kubernetes Pod CIDR exhaustion.
Test your subnetting reflexes with 4 specialized training modes — 60-second Blitz, Precision Sprint, Binary Flipper, and AWS VPC Architect. 100% free. Zero logins. Zero tracking.
Play Free in Your Browser →This subnetting cheat sheet teaches CIDR mental math with the Magic Number method, explains why AWS reserves five addresses in every subnet, and shows how pod IP exhaustion bites EKS clusters. A speed game lets you practice.
1. Why CIDR Math Still Breaks Cloud Infrastructure
In traditional on-premises networking, running out of IP addresses was a nuisance. In modern cloud-native environments, an undersized CIDR block is an existential architectural failure.
The High-Density Pod Trap
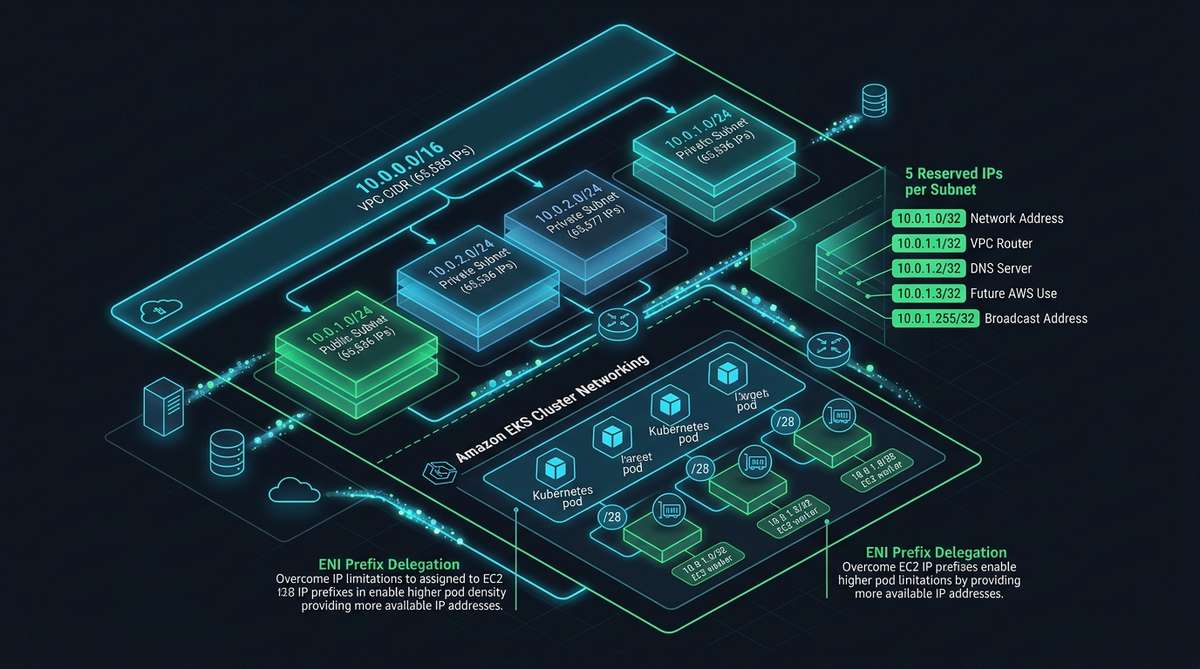
Unlike overlay networks (Flannel/VXLAN) that encapsulate packets in tunnels, the AWS VPC CNI assigns real private IPv4 addresses from the node's underlying VPC subnet directly to every Pod.
- An
m5.2xlargeinstance can host up to 58 pods across multiple ENIs. - A conservatively sized
/26subnet has only 59 usable IPs in AWS. - Two worker nodes will consume 100% of the available IP pool.
When the cluster autoscaler tries to spin up a third node, pods fail with:
failed to assign an IP address to container: no free IP addresses available in subnetPods remain stuck in ContainerCreating or CrashLoopBackOff. Autoscaling completely halts.
Real-World CIDR Failure Modes
| Scenario | Root Cause | Production Impact |
|---|---|---|
EKS Pods stuck in ContainerCreating | /26 subnet exhausted by 2 worker nodes | Autoscaling halted, revenue loss |
| Transit Gateway route conflicts | Overlapping CIDR blocks in spoke VPCs | Cross-account connectivity broken |
| VPC Peering setup failure | Overlapping RFC 1918 ranges | Terraform apply fails |
| Direct Connect BGP failure | Non-summarizable CIDR advertisements | Hybrid cloud network partitioned |
⚠️ Key Production Insight: You cannot easily resize an existing VPC subnet without recreating routing tables, re-attaching ENIs, or orchestrating dual-CIDR secondary VPC migrations. Understand your address math before applying Terraform.
The 970+ Incident Handbook & K8s Runbooks are exclusive to subscribers — unlock for FREE
Get battle-tested production runbooks, AWS architecture blueprints, and zero-downtime CI/CD post-mortems sent directly to your inbox. 100% free, no spam.
2. RFC 1918 vs. AWS Cloud Reality: The 5 Reserved IPs
In standard RFC 1918 networking, every IPv4 subnet reserves exactly 2 IP addresses:
- Network Address (Host bits all 0): Identifies the network itself.
- Directed Broadcast Address (Host bits all 1): Broadcasts to every host.
Usable Hosts (RFC 1918) = 2^(32 - Prefix) - 2However, AWS reserves 5 IP addresses in every single VPC subnet, regardless of prefix size:
| Reserved IP Slot | Address in 10.0.0.0/24 | AWS Architectural Purpose |
|---|---|---|
| First Address | 10.0.0.0 | Network Address (RFC standard) |
| Second Address | 10.0.0.1 | VPC Router (default gateway) |
| Third Address | 10.0.0.2 | AmazonProvidedDNS (Route 53 Resolver) |
| Fourth Address | 10.0.0.3 | AWS Future Internal Use |
| Last Address | 10.0.0.255 | Broadcast (reserved, not used) |
Standard RFC vs. AWS: Side-by-Side
| Feature | Standard RFC 1918 | AWS VPC |
|---|---|---|
| Reserved Addresses | 2 per subnet | 5 per subnet |
| Usable Hosts Formula | 2^(32-prefix) - 2 | 2^(32-prefix) - 5 |
/28 Block Usable IPs | 14 | 11 (21% capacity penalty) |
/24 Block Usable IPs | 254 | 251 |
| Minimum Subnet Size | /30 (2 usable) | /28 (AWS enforced minimum) |
| Broadcast Support | Native L2/L3 broadcast | No broadcast (address reserved) |
⚠️ The Cost of Forgetting: If you allocate a /28 expecting 14 usable IPs (16 − 2 = 14), AWS leaves you with only 11 usable IPs (16 − 5 = 11). If your auto-scaling group requests 12 instances, provisioning crashes immediately.
3. The 3-Second Mental Math Framework: The Magic Number
Most networking courses force students to convert octets into 8-bit binary strings, perform bitwise AND operations, and convert back. Under live interview pressure or a production incident, this is far too slow.
Senior network architects rely on a simple mental shortcut: the Magic Number Method.
Magic Number = 256 − Interesting Octet Mask
The "Interesting Octet" is the specific octet where the subnet mask changes from 255 to something other than 0.
Worked Example: Solving 192.168.1.75/27 in 3 Seconds
Step 1 — Find the Interesting Octet & Mask:
A /24 uses octets 1-3 → 255.255.255.0.
A /27 adds 3 more bits into the 4th octet: 128 + 64 + 32 = 224.
Full mask: 255.255.255.224.
Step 2 — Apply Magic Number:
256 − 224 = 32
Step 3 — Step through subnet boundaries (increments of 32):
| Subnet | Network Address | Broadcast Address |
|---|---|---|
| Subnet 0 | .0 | .31 |
| Subnet 1 | .32 | .63 |
| Subnet 2 ✓ | .64 | .95 |
| Subnet 3 | .96 | .127 |
Step 4 — Pinpoint 192.168.1.75:
Falls between .64 and .95 → Subnet 2.
- Network Address:
192.168.1.64 - First Usable Host:
192.168.1.65 - Last Usable Host:
192.168.1.94 - Broadcast Address:
192.168.1.95 - RFC Usable Hosts: 32 − 2 = 30
Complete CIDR Cheat Sheet (4th Octet Subnets)
| CIDR Prefix | Subnet Mask | Magic Number | RFC Usable | AWS Usable |
|---|---|---|---|---|
| /24 | 255.255.255.0 | 256 | 254 | 251 |
| /25 | 255.255.255.128 | 128 | 126 | 123 |
| /26 | 255.255.255.192 | 64 | 62 | 59 |
| /27 | 255.255.255.224 | 32 | 30 | 25 |
| /28 | 255.255.255.240 | 16 | 14 | 11 |
| /29 | 255.255.255.248 | 8 | 6 | 3 |
| /30 | 255.255.255.252 | 4 | 2 | 0 (min /28) |
💡 Interview Tip: Interviewers at top cloud-native companies (Stripe, Datadog, Cloudflare) specifically test subnetting proficiency for senior DevOps and platform engineering roles. The Magic Number method lets you answer instantly — no pen or paper required.
4. Gamifying Systems Engineering: 4 Arcade Training Modes
Reading an article provides passive familiarity. Under technical interview pressure or during a live production incident, you need reflexive recall — the kind of muscle memory only active practice builds.
I built the CIDR & Subnetting Speed Challenge with four specialized drill modes:
5. Engineering Under the Hood: Zero-Dependency, Web Audio API
When building interactive tools for engineers, bloated frameworks and multi-megabyte asset downloads ruin the experience. The arcade was built with strict performance-first principles:
Synthesized Native Audio (Zero MP3 Downloads)
All sound effects — correct chimes, streak chords, countdown ticks, buzzer tones — are synthesized natively via the browser's Web Audio API:
// Native Web Audio Synthesizer: Zero external asset downloads
const audioCtx = new (window.AudioContext || window.webkitAudioContext)();

function playTone(freq, type, duration, delay = 0) {
  if (!soundEnabled) return;
  const osc = audioCtx.createOscillator();
  const gain = audioCtx.createGain();

  osc.type = type; // 'sine' | 'triangle' | 'square'
  osc.frequency.setValueAtTime(freq, audioCtx.currentTime + delay);

  // Exponential decay prevents clipping clicks
  gain.gain.setValueAtTime(0.15, audioCtx.currentTime + delay);
  gain.gain.exponentialRampToValueAtTime(0.001, audioCtx.currentTime + delay + duration);

  osc.connect(gain);
  gain.connect(audioCtx.destination);
  osc.start(audioCtx.currentTime + delay);
  osc.stop(audioCtx.currentTime + delay + duration);
}

// 3-tone ascending chord on streak milestones
function playStreakChime() {
  playTone(523.25, 'sine', 0.15, 0.0);  // C5
  playTone(659.25, 'sine', 0.15, 0.08); // E5
  playTone(783.99, 'sine', 0.25, 0.16); // G5
}
Performance Metrics
| Metric | Target | Achieved |
|---|---|---|
| First Contentful Paint | < 300ms | < 200ms |
| Total Bundle Weight | < 100KB | < 40KB |
| External JS Dependencies | 0 | 0 |
| Mobile Responsiveness | Full | Full |
6. EKS Prefix Delegation 2025: Fix IP Exhaustion Without Resizing Subnets
If you're already running an EKS cluster with undersized subnets and can't easily re-architect your VPC, EKS prefix delegation is the fastest production fix available in 2025. It's the AWS-recommended solution for Kubernetes Pod CIDR exhaustion.
How Prefix Delegation Solves IP Exhaustion
Instead of assigning individual /32 IPs to each pod, the VPC CNI assigns a /28 IPv4 prefix (16 addresses) to each ENI on your EC2 node.
| Instance Type | Standard Max Pods | With Prefix Delegation | Improvement |
|---|---|---|---|
m5.large | 29 pods | 110 pods | 3.8× |
m5.2xlarge | 58 pods | 110 pods | 1.9× |
m5.4xlarge | 234 pods | 234 pods | Capped by AWS |
Enable Prefix Delegation (One Command)
# Step 1: Enable prefix delegation on the aws-node DaemonSet
kubectl set env daemonset aws-node \
  -n kube-system \
  ENABLE_PREFIX_DELEGATION=true

# Step 2: Set warm prefix target (optional, reduces startup latency)
kubectl set env daemonset aws-node \
  -n kube-system \
  WARM_PREFIX_TARGET=1

# Step 3: Verify — nodes should now show higher pod capacity
kubectl get nodes -o custom-columns=\
'NAME:.metadata.name,CAPACITY:.status.capacity.pods'
⚠️ Requires: VPC CNI v1.9+, EKS 1.21+, and instance types that support multiple ENIs. Nitro-based instances (m5, c5, r5 families) are fully supported.
7. AWS IPAM 2025: Automated IP Address Management for Multi-Account VPCs
As organizations scale to dozens of VPCs across multiple AWS accounts and regions, manually tracking CIDR allocations in spreadsheets becomes a disaster waiting to happen. AWS IP Address Manager (IPAM) solves this at scale.
What AWS IPAM Does
- Centralized CIDR tracking — Single pane of glass across all VPCs, accounts, and regions.
- Automated allocation — Assigns CIDR blocks to new VPCs from a pre-defined pool, preventing overlaps.
- Compliance auditing — Flags unallocated, over-utilized, or overlapping CIDRs.
- Transit Gateway safety — Ensures spoke VPCs never receive overlapping CIDRs that would break TGW routing.
When You Need IPAM
| Trigger | IPAM Recommendation |
|---|---|
| More than 5 VPCs in your org | ✅ Use IPAM pools |
| Multiple AWS accounts (Organizations) | ✅ Use IPAM with Resource Access Manager |
| Transit Gateway hub-and-spoke | ✅ Critical — prevents CIDR conflicts |
| VPC peering across teams | ✅ Prevents the CIDR clash |
| Single VPC, single account | 🟡 Optional — manual tracking works |
# Terraform: Create an IPAM pool for production VPCs
resource "aws_vpc_ipam" "main" {
  operating_regions {
    region_name = "us-east-1"
  }
}

resource "aws_vpc_ipam_pool" "prod" {
  address_family = "ipv4"
  ipam_scope_id  = aws_vpc_ipam.main.private_default_scope_id
  locale         = "us-east-1"
}

resource "aws_vpc_ipam_pool_cidr" "prod_cidr" {
  ipam_pool_id = aws_vpc_ipam_pool.prod.id
  cidr         = "10.0.0.0/8"  # Master pool — all VPCs carved from here
}

# VPC auto-gets a /24 from the IPAM pool — no manual CIDR selection needed
resource "aws_vpc" "app" {
  ipv4_ipam_pool_id   = aws_vpc_ipam_pool.prod.id
  ipv4_netmask_length = 24
}
8. Subnetting for CCNA, Network+ & CKA Certification 2025 — Plus IPv6
CCNA & Network+ Subnetting Exam Tips
Subnetting questions appear in every CCNA (200-301) and Network+ (N10-009) exam. The question formats you'll encounter:
- Given an IP and prefix, find the network address, broadcast, first/last usable host
- Given a requirement (e.g., "need 50 hosts"), find the minimum CIDR prefix
- Given an address range, determine if two IPs are in the same subnet
- Calculate the number of subnets created by borrowing N bits
The Magic Number method solves all four types in under 5 seconds. Practice with the CIDR Speed Challenge until it's automatic.
CKA Exam Networking (Kubernetes Certified Administrator)
For the CKA exam, subnetting knowledge is tested through:
- Configuring
--pod-network-cidrand--service-cidrduringkubeadm init - Understanding why Pod CIDRs must not overlap with node or service CIDRs
- Troubleshooting CNI connectivity failures caused by exhausted or overlapping CIDR ranges
# CKA Exam: Initialize cluster with non-overlapping CIDRs
kubeadm init \
  --pod-network-cidr=192.168.0.0/16 \
  --service-cidr=10.96.0.0/12

# Verify pod and service CIDRs don't overlap with your node subnet
kubectl cluster-info dump | grep -E "podCIDR|serviceCluster"IPv6: The Long-Term Solution to IP Exhaustion
IPv6 adoption in AWS VPC is the #1 trending topic for cloud architects in 2025. With a /56 block per VPC providing 4.7 × 10²⁴ addresses, IP exhaustion becomes mathematically impossible.
| Aspect | IPv4 VPC | IPv6 VPC (2025 Best Practice) |
|---|---|---|
| Address Space | RFC 1918 limited (~17M private IPs) | Effectively unlimited (/56 per VPC) |
| EKS Pod IPs | From VPC subnet (exhaustible) | From /80 prefix per node (infinite) |
| NAT Gateway cost | Required for private outbound | Not needed for IPv6 egress |
| AWS IPAM support | Full support | Full support (BYOIP IPv6) |
| AWS minimum subnet | /28 (11 usable) | /64 (1.8 × 10¹⁹ addresses) |
# Enable IPv6 on existing VPC and subnets (Terraform)
resource "aws_vpc" "main" {
  cidr_block                       = "10.0.0.0/16"
  assign_generated_ipv6_cidr_block = true  # AWS assigns a /56
}

resource "aws_subnet" "app" {
  vpc_id                          = aws_vpc.main.id
  cidr_block                      = "10.0.1.0/24"
  ipv6_cidr_block                 = cidrsubnet(aws_vpc.main.ipv6_cidr_block, 8, 1)
  assign_ipv6_address_on_creation = true
}
9. Conclusion: Active Recall Beats Passive Documentation
Subnetting is not about rote memorization or doing tedious binary arithmetic on scratch paper. It is about recognizing block sizes, predicting capacity constraints, and avoiding cloud architectural traps before they reach production.
The next time an interviewer asks you to subnet a /21 across three AZs, or your Kubernetes nodes start dropping pods due to CNI pool starvation, you won't need to reach for a calculator.
Great platform engineers don't rely on crutches for foundational networking math. Master the Magic Number, account for cloud provider reservations, and drill your reflexes until CIDR calculations become second nature.
Ready to Test Your Networking Speed?
Play the CIDR & Subnetting Speed Challenge — completely free, zero logins, zero tracking. Drop your highest Blitz score and streak in the comments!
🎮 Play Free at games.naveedkumbhar.com →Subnetting Cheat Sheet: Key Takeaways
This guide to subnetting cheat sheet covers the sections below, so you can jump straight to the part you need.
- 1. Why CIDR Math Still Breaks Cloud Infrastructure
- 2. RFC 1918 vs. AWS Cloud Reality: The 5 Reserved IPs
- 3. The 3-Second Mental Math Framework: The Magic Number
- 4. Gamifying Systems Engineering: 4 Arcade Training Modes
- 5. Engineering Under the Hood: Zero-Dependency, Web Audio API
- 6. EKS Prefix Delegation 2025: Fix IP Exhaustion Without Resizing Subnets
- 7. AWS IPAM 2025: Automated IP Address Management for Multi-Account VPCs
Frequently Asked Questions — AWS Subnetting & CIDR 2025
Why does AWS reserve 5 IP addresses per subnet instead of 2?
AWS reserves 5 addresses per VPC subnet: network (.0), VPC router (.1), AmazonProvidedDNS (.2), future use (.3), and broadcast (last). Standard RFC 1918 only reserves 2. This means a /28 gives you only 11 usable IPs in AWS instead of 14.
What is the Magic Number method for subnetting?
Magic Number = 256 − Interesting Octet Mask. The interesting octet is where the mask is neither 255 nor 0. The magic number is the block size — subnets step in multiples of it. For /27: mask byte is 224, so 256 − 224 = 32. Subnets step by 32: .0, .32, .64, .96, etc.
How does Kubernetes Pod CIDR exhaustion happen on AWS EKS?
The AWS VPC CNI assigns real VPC subnet IPs directly to each Pod. An m5.2xlarge node can host up to 58 pods. A /26 subnet (59 usable IPs in AWS) is fully exhausted by just 2 high-density worker nodes, causing new pods to fail with "no free IP addresses available in subnet".
What is the minimum subnet size in AWS VPC?
AWS enforces a minimum subnet size of /28. A /28 block has 16 total addresses, of which AWS reserves 5, leaving only 11 usable IPs. For EKS node subnets always use /24 or larger.
What is EKS prefix delegation and how does it fix IP exhaustion in 2025?
EKS prefix delegation (VPC CNI v1.9+) assigns /28 IPv4 prefixes to EC2 ENIs instead of single IPs, increasing pod capacity per node by up to 16×. An m5.large can host 110 pods instead of 29. Enable with: kubectl set env daemonset aws-node -n kube-system ENABLE_PREFIX_DELEGATION=true
What is AWS IPAM and when should I use it?
AWS IP Address Manager (IPAM) automatically tracks, audits, and allocates CIDR blocks across multi-account, multi-region AWS environments. Use it when you have more than 5 VPCs, multiple AWS accounts, or Transit Gateway hub-and-spoke architectures where CIDR overlaps would break routing.
How do I practice subnetting for CCNA or Network+ certification in 2025?
Practice with timed repetition drills using the Magic Number method. The free CIDR & Subnetting Speed Challenge has a 60-second Speed Blitz, 10-question Precision Sprint, and 32-bit Binary Flipper — directly mapping to CCNA (200-301) and Network+ (N10-009) exam question formats.
Related Articles