This comprehensive subnetting cheat sheet explores the mathematical foundations of CIDR networking and explains exactly What AWS IPAM Does to eliminate manual IP management across enterprise clouds. Miscalculating subnet boundaries or deploying overlapping IP blocks causes severe cloud outages, from broken Transit Gateway routing to sudden Kubernetes Pod IP exhaustion. Here you will learn the three-second Magic Number mental math method, examine why AWS reserves five IP addresses instead of two, configure EKS prefix delegation, and automate multi-account VPC IP allocation using AWS IPAM.
Test your subnetting reflexes with 4 specialized training modes: 60-Second Blitz, Precision Sprint, Binary Flipper, and AWS VPC Architect. 100% free with zero tracking. When architecting multi-AZ VPC subnets for early-stage teams, review our foundational guide to AWS infrastructure for startups.
Play Free in Your Browser →1. Why CIDR Math Still Breaks Cloud Infrastructure and What AWS IPAM Does (Subnetting Cheat Sheet)
Understanding what AWS IPAM does begins with recognizing how manual subnet math causes silent cloud outages. When teams deploy containerized workloads or multi-account VPC networks without automated IP management, overlapping CIDR ranges halt Transit Gateway attachments, starve Kubernetes pods of host IPs, and require emergency subnet rebuilding under intense production pressure.
In traditional on-premises networking, running out of IP addresses was an operational annoyance that meant submitting a ticket to the network team. In modern cloud-native environments, an undersized CIDR block is an existential architectural failure. Applying effective vpc cidr planning tips and mastering cidr math shortcuts early prevents expensive refactoring when deploying high-density container platforms. Before provisioning VPC subnets in production, verify your network boundaries with our client-side CIDR subnet calculator to inspect usable IP allocations and reserved ranges.
The High-Density Pod Trap
Unlike overlay networks that encapsulate packets inside VXLAN tunnels, the AWS VPC CNI assigns real private IPv4 addresses from the node's underlying VPC subnet directly to every Pod, making eks pod ip exhaustion a frequent failure mode in high-density clusters:
- An
m5.2xlargeinstance can host up to 58 pods across multiple Elastic Network Interfaces (ENIs). - A conservatively sized
/26subnet provides only 59 usable IPs in AWS after accounting for reserved addresses. - Two active worker nodes will consume 100% of the available IP pool.
When the cluster autoscaler attempts to spin up a third node, pods fail with:
failed to assign an IP address to container: no free IP addresses available in subnetPods remain stuck in ContainerCreating or CrashLoopBackOff. Cluster autoscaling completely halts.
Real-World CIDR Failure Modes
| Scenario | Root Cause | Production Impact |
|---|---|---|
| EKS Pods stuck in ContainerCreating | /26 subnet exhausted by 2 worker nodes |
Autoscaling halted, deployment rollouts stall |
| Transit Gateway route conflicts | Overlapping CIDR blocks in spoke VPCs | Cross-account connectivity broken silently |
| VPC Peering setup failure | Overlapping RFC 1918 ranges between VPCs | Terraform apply fails with route table conflict |
| Direct Connect BGP failure | Non-summarizable CIDR advertisements | Hybrid cloud network routes partition |
To see how senior platform engineers resolve these failure modes during live incidents, explore our technical runbooks on resolving overlapping VPC CIDR blocks and AWS Transit Gateway vs VPC Peering architectural choice. For end-to-end Kubernetes reliability, check our Kubernetes pod CIDR toolkit.
Resolver for CIDR Errors: Diagnostic Commands and Triage
When automated infrastructure pipelines fail with routing collisions, engineers need an immediate resolver for cidr errors and a clear procedure for how to detect overlapping cidr blocks. Running targeted AWS CLI queries surfaces overlapping allocations and reveals available subnet headroom before deploying new services:
# Query all VPC CIDRs across an AWS region to identify route collisions
aws ec2 describe-vpcs \
  --query "Vpcs[*].{VpcId:VpcId,CidrBlock:CidrBlock,State:State,Tags:Tags[?Key=='Name'].Value|[0]}" \
  --output table

# Check available IPv4 address headroom across active VPC subnets
aws ec2 describe-subnets \
  --filters "Name=vpc-id,Values=vpc-0a1b2c3d4e5f6g7h8" \
  --query "Subnets[*].{SubnetId:SubnetId,CIDR:CidrBlock,AvailableIPs:AvailableIpAddressCount,AZ:AvailabilityZone}" \
  --output table
Implementing proper overlapping cidr resolution is critical when planning an enterprise cloud migration. When debugging container networking issues and cluster pods during incidents, keep our production Kubectl Cheat Sheet handy for cluster triage commands. If you are preparing a large-scale data center evacuation, review our zero-downtime AWS migration playbook to ensure that hybrid transit networks remain completely non-conflicting.
The 970+ Incident Handbook & K8s Runbooks are exclusive to subscribers — unlock for FREE
Get battle-tested production runbooks, AWS architecture blueprints, and zero-downtime CI/CD post-mortems sent directly to your inbox. 100% free, no spam.
2. RFC 1918 vs. AWS Cloud Reality: The 5 Reserved IPs
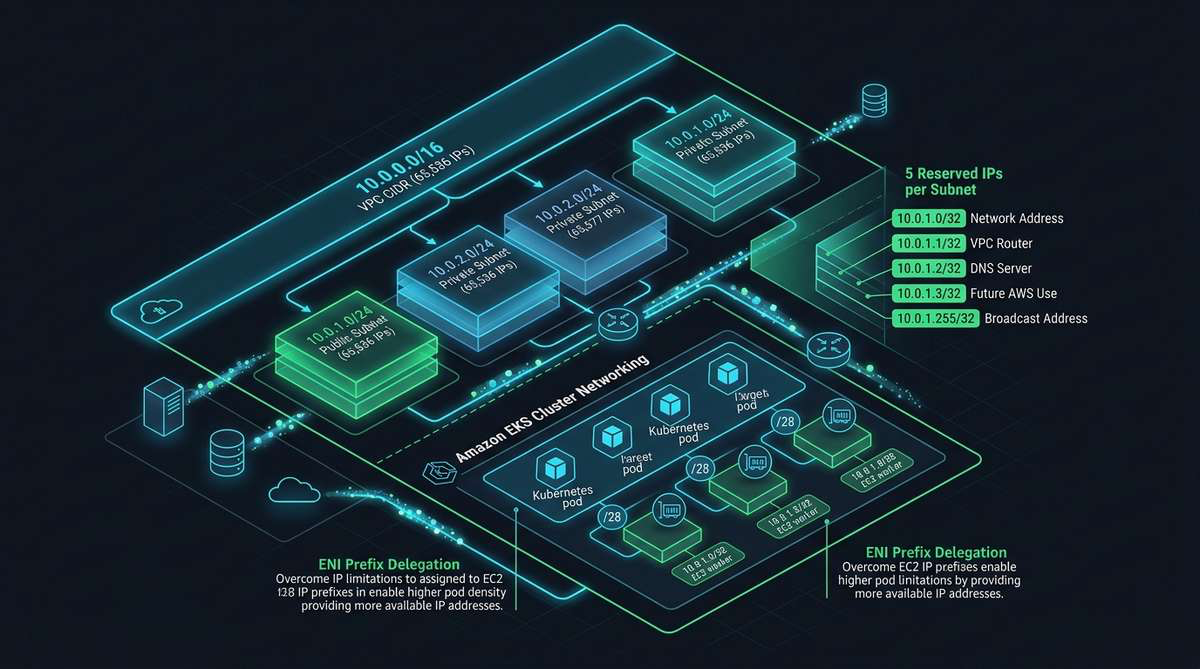
Standard RFC 1918 networks reserve only two IP addresses per subnet: the network identifier and the broadcast address. In contrast, Amazon Web Services reserves five IP addresses across every VPC subnet for the network wire, VPC router, DNS resolver, future capabilities, and broadcast. Forgetting this disparity creates instant container deployment failures.
In standard on-premises networking (RFC 1918), usable hosts in any subnet equal 2^(32 − prefix) − 2. You lose two addresses: the first for the network ID, and the last for the broadcast address. In Amazon Web Services, you lose the aws 5 reserved ip addresses in every subnet. AWS reserves the first four IP addresses and the last IP address:
Standard RFC vs. AWS: Side-by-Side
| IP Offset | Example (10.0.1.0/24) | AWS Reserved Purpose |
|---|---|---|
| .0 | 10.0.1.0 |
Network address (wire ID). |
| .1 | 10.0.1.1 |
VPC default router / gateway. |
| .2 | 10.0.1.2 |
Amazon DNS resolver (base + 2 or 169.254.169.253). |
| .3 | 10.0.1.3 |
AWS reserved for future internal capabilities. |
| .255 | 10.0.1.255 |
Network broadcast address (VPC does not support broadcast). |
Comparing these allocations side by side highlights that a /28 subnet (16 total addresses) has only 11 usable IPs, and a /29 subnet (8 total addresses) provides only 3 usable IPs. In AWS, /28 is the smallest permitted VPC subnet size. To see how these reserved IPs and subnets are provisioned via infrastructure as code, work through our hands-on Terraform AWS EKS Module Lab.
3. The 3-Second Mental Math Framework: The Magic Number
The Magic Number method provides a rapid mental math technique for solving CIDR subnet boundaries in under three seconds without calculators. Subtracting the interesting octet subnet mask from two hundred fifty-six yields the step size. Subnet network boundaries increment in multiples of this step size, instantly revealing valid host and broadcast ranges.
Every IPv4 subnet problem boils down to identifying which of the four octets is changing (the "interesting octet") and finding the step size between subnets. The subnetting magic number formula is universal:
Magic Number = 256 − Interesting Octet Mask
The Magic Number is your subnet step size. All subnets in that octet step by exact multiples of this number, starting at 0. Consider this practical worked example:
Worked Example: Solving 192.168.1.75/27 in 3 Seconds
- Find the interesting octet:
/27lies in the 4th octet (24 + 3 bits borrowed). The mask value is255.255.255.224. - Calculate the Magic Number:
256 − 224 = 32. Subnets step in multiples of 32 (.0, .32, .64, .96...). - Locate the target IP: Host
.75falls between.64and.96. - Extract boundaries instantly:
- Network Address:
192.168.1.64 - First Usable Host:
192.168.1.65(AWS reserves up to .67) - Broadcast Address:
192.168.1.95(one below the next subnet) - Last Usable Host:
192.168.1.94
- Network Address:
Complete CIDR Cheat Sheet (4th Octet Subnets)
This operational subnetting cheat sheet ipv4 reference details 4th octet subnets from /25 through /30. Platform engineers use this cidr cheat sheet ipv4, subnet mask cheat sheet, and subnetting cheat sheet chart to size VPC subnets, calculate host capacities, and verify network broadcast boundaries without calculator dependency:
| Prefix | Subnet Mask | Wildcard Mask | Magic Number | Total IPs | RFC 1918 Usable | AWS Usable |
|---|---|---|---|---|---|---|
| /25 | 255.255.255.128 |
0.0.0.127 |
128 | 128 | 126 | 123 |
| /26 | 255.255.255.192 |
0.0.0.63 |
64 | 64 | 62 | 59 |
| /27 | 255.255.255.224 |
0.0.0.31 |
32 | 32 | 30 | 27 |
| /28 | 255.255.255.240 |
0.0.0.15 |
16 | 16 | 14 | 11 |
| /29 | 255.255.255.248 |
0.0.0.7 |
8 | 8 | 6 | 3 (Non-VPC) |
| /30 | 255.255.255.252 |
0.0.0.3 |
4 | 4 | 2 | 0 (Non-VPC) |
The subnetting cheat sheet table above incorporates the inverse subnet cheat sheet wildcard mask, an essential value for Cisco access control lists and firewall policies. Analyzing the exact subnet cheat sheet usable ip column reveals why AWS VPC boundaries require rigorous planning: a subnet cheat sheet 29 network yields 6 usable hosts in data centers, but only 3 usable hosts in AWS, making /28 the absolute minimum allowed subnet in AWS VPC infrastructure.
For engineers accustomed to the classic subnetting cheat sheet cisco curriculum, the Magic Number method matches exam blueprints while directly applying to cloud operations. While older sysadmin playbooks tracked allocations in a static subnetting cheat sheet excel sheet, dynamic multi-account environments demand programmatic IPAM. Online discussions on subnetting cheat sheet reddit engineering communities emphasize that memorizing 4th-octet increments prevents catastrophic routing collisions faster than searching for a subnetting cheat sheet youtube tutorial or clicking through a subnet cheat sheet calculator during a live outage. If you manage automated host provisioning across these CIDRs, bookmark our ansible commands cheat sheet for inventory and playbook orchestration. To prepare for modern dual-stack networks, review our subnet cheat sheet ipv6 considerations below where standard /64 subnets eliminate IP scarcity completely.
4. IPAM vs Subnet Planning: Comparing Manual and Automated CIDR Workflows
Evaluating ipam vs subnet planning highlights the stark operational boundary between static spreadsheet documentation and programmatic cloud networking. While manual subnet planning works for isolated single-VPC deployments, it collapses under multi-account scale. Automated IPAM continuously tracks allocations, enforces boundary constraints, and prevents overlapping CIDR reservations across complex AWS Organizations.
When platform teams weigh ipam vs subnet planning, the decision hinges on operational scale, velocity, and multi-tenant isolation requirements:
| Dimension | Manual Subnet Planning | Automated AWS IPAM |
|---|---|---|
| Allocation Speed | Slow (Ticket-based spreadsheet lookups) | Instant (API-driven dynamic allocation) |
| Overlap Prevention | Error-prone (Requires manual discipline) | Strict (Pool enforcement guarantees uniqueness) |
| Multi-Account Support | Siloed across accounts and regions | Native AWS Organizations integration |
| Compliance & Auditing | Manual periodic documentation audits | Continuous CloudWatch metrics & CloudTrail |
When standardizing IaC deployments across staging and production clusters, teams reference Terraform architecture for production AWS SaaS platforms to declare CIDR pools alongside our complete blueprint for deploying Kubernetes on AWS.
4. Gamifying Systems Engineering: 4 Arcade Training Modes
Gamified active recall exercises convert abstract binary arithmetic into intuitive operational reflexes during high-stress production troubleshooting. Drilling with timed speed challenges tests mask conversions, usable host calculations, network boundaries, and multi-tier VPC provisioning rules. Practicing these scenarios trains engineers to identify overlapping CIDRs and undersized Kubernetes subnets on whiteboards and terminal prompts.
Passive reading cannot build reflexive operational speed. The free browser-based CIDR & Subnetting Speed Challenge provides four focused practice modules:
⚡ 60-Second Speed Blitz
Rapid-fire questions on masks, usable host counts, and network boundaries under a tight 60-second countdown with combo multiplier scores.
Play Blitz Mode →🎯 10-Question Precision Sprint
Untimed deliberate practice covering non-standard CIDR boundaries (/21, /23, /28) with detailed post-drill performance diagnostics.
Play Precision Mode →🎛️ 32-Bit Binary Flipper
Interactive bit toggling across all four octets. Watch dotted decimal masks, wildcard masks, and host counts update in real time.
Launch Binary Flipper →☁️ AWS VPC Architect
Carve non-overlapping subnets across Web, Application, and Database tiers spanning 3 Availability Zones while accounting for AWS reserved IPs.
Launch VPC Challenge →5. Engineering Under the Hood: Zero-Dependency, Web Audio API
Modern browser-based engineering drills should operate with zero external runtime dependencies and instant interactive responsiveness. Using the native Web Audio API allows web applications to synthesize responsive audio tones and milestone chimes entirely from mathematical waveforms. This architecture eliminates multi-megabyte sound file downloads, ensuring sub-two-hundred-millisecond page loads on mobile and desktop browsers alike.
When building tools for platform engineers, bloated runtimes and multi-megabyte asset bundles degrade the user experience. All sound effects in the speed game are synthesized on the fly via the browser's native Web Audio API:
Synthesized Native Audio (Zero MP3 Downloads)
// Native Web Audio Synthesizer: Zero external asset downloads
const audioCtx = new (window.AudioContext || window.webkitAudioContext)();

function playTone(freq, type, duration, delay = 0) {
  const osc = audioCtx.createOscillator();
  const gain = audioCtx.createGain();

  osc.type = type; // 'sine' | 'triangle' | 'square'
  osc.frequency.setValueAtTime(freq, audioCtx.currentTime + delay);

  // Exponential decay prevents clipping clicks
  gain.gain.setValueAtTime(0.15, audioCtx.currentTime + delay);
  gain.gain.exponentialRampToValueAtTime(0.001, audioCtx.currentTime + delay + duration);

  osc.connect(gain);
  gain.connect(audioCtx.destination);
  osc.start(audioCtx.currentTime + delay);
  osc.stop(audioCtx.currentTime + delay + duration);
}

// 3-tone ascending chime played on streak milestones
function playStreakChime() {
  playTone(523.25, 'sine', 0.15, 0.0);  // C5
  playTone(659.25, 'sine', 0.15, 0.08); // E5
  playTone(783.99, 'sine', 0.25, 0.16); // G5
}
Performance Metrics
| Metric | Target | Achieved |
|---|---|---|
| First Contentful Paint | < 300ms | < 200ms |
| Total Bundle Weight | < 100KB | < 40KB |
| External JS Dependencies | 0 | 0 |
| Mobile Responsiveness | Full | Full |
Similar to lightweight event-driven runtimes, observing clean ipam api usage patterns allows scripts to query allocation telemetry without blocking client render cycles.
6. EKS Prefix Delegation 2025: Fix IP Exhaustion Without Resizing Subnets
Modern network design for EKS clusters uses prefix delegation to eliminate pod IP exhaustion without resizing underlying subnets. By assigning sixteen-address IPv4 prefixes directly to secondary elastic network interfaces rather than single IP addresses, Kubernetes worker nodes dramatically expand container density. This architectural approach allows smaller EC2 instances to host enterprise pod volumes.
Architecting scalable network design for eks requires addressing the relationship between EC2 instance types, ENI slots, and maximum pod allocations. For engineers managing pod networking in production, test your command-line troubleshooting reflexes in our kubectl practice game when cluster pods fail to schedule due to CNI or IP exhaustion. Examining prefix delegation eks depth reveals how the AWS VPC CNI assigns a /28 IPv4 prefix (16 IP addresses) to each ENI slot instead of an individual /32 IP address:
How Prefix Delegation Solves IP Exhaustion
| Instance Type | Standard Max Pods | With Prefix Delegation | Density Improvement |
|---|---|---|---|
m5.large |
29 pods | 110 pods | 3.8x capacity |
m5.2xlarge |
58 pods | 110 pods | 1.9x capacity |
m5.4xlarge |
234 pods | 234 pods | Capped by node limit |
Enabling prefix delegation on EKS takes three straightforward commands:
# Enable prefix delegation on the aws-node DaemonSet
kubectl set env daemonset aws-node \
  -n kube-system \
  ENABLE_PREFIX_DELEGATION=true

# Set warm prefix target to prevent cold-start pod scheduling latency
kubectl set env daemonset aws-node \
  -n kube-system \
  WARM_PREFIX_TARGET=1

# Verify that worker nodes report updated allocatable pod capacity
kubectl get nodes -o custom-columns='NAME:.metadata.name,CAPACITY:.status.capacity.pods'
When underlying subnets cannot be resized to accommodate delegated prefixes, allocating a secondary cidr block for eks (such as from the 100.64.0.0/16 CGNAT range) lets pod ENIs pull from a dedicated address pool while preserving primary VPC IPs for load balancers. When transitioning multi-container services from local environments to cluster namespaces, convert your compose stacks into Deployments with our Docker Compose to Kubernetes migration tool, and enforce granular ingress and egress policies with our Kubernetes NetworkPolicy Guide or client-side network policy generator.
7. AWS IPAM 2025: Automated IP Address Management for Multi-Account VPCs
Analyzing what AWS IPAM does demonstrates how centralized address tracking replaces fragile spreadsheets across multi-account enterprise clouds. Operating through AWS Organizations and Resource Access Manager, the AWS IPAM service assigns non-overlapping CIDR blocks to new VPCs, monitors pool utilization, logs compliance audit trails, and guarantees non-conflicting routing across Transit Gateway spoke topologies.
As cloud platforms expand beyond individual development accounts, managing IP allocations through ad-hoc documentation collapses. Organizations adopting multi account vpc ipam utilize the managed aws ipam service to centralize CIDR governance across regions and accounts. Following the official aws ipam integration user guide and AWS best practices, platform engineers establish an aws vpc ipam pool hierarchy implementing proven ipam pool design best practices:
Top-Level Pool (Global Supernet)
Defines the master corporate supernet (e.g., 10.0.0.0/8). Managed centrally by the cloud platform team inside a delegated network administration account.
Regional Pools (Scope Isolation)
Carves out dedicated regional CIDRs (e.g., 10.10.0.0/16 for us-east-1 and 10.20.0.0/16 for eu-west-1) to support clean route aggregation.
Environment Pools (Dev, Staging, Prod)
Enforces environment-specific rules and tagging. VPCs created by member accounts request a prefix length (e.g., /24) and receive a guaranteed non-overlapping allocation.
As documented in official aws ipam documentation, this cloud-native aws ipam tool integrates with AWS Resource Access Manager (RAM) to share pools across organizational accounts without exposing administrative credentials. Platform teams declare IPAM resources directly in Terraform:
# Provision AWS IPAM instance with operational regions
resource "aws_vpc_ipam" "main" {
  description = "Centralized enterprise VPC IPAM"
  operating_regions {
    region_name = "us-east-1"
  }
}

# Define root production pool
resource "aws_vpc_ipam_pool" "prod" {
  description        = "Production VPC root pool"
  address_family     = "ipv4"
  ipam_scope_id      = aws_vpc_ipam.main.private_default_scope_id
  locale             = "us-east-1"
  auto_import        = true
}

resource "aws_vpc_ipam_pool_cidr" "prod_cidr" {
  ipam_pool_id = aws_vpc_ipam_pool.prod.id
  cidr         = "10.100.0.0/16"
}

# New VPC auto-allocates a /24 from the IPAM pool with zero manual CIDR math
resource "aws_vpc" "app" {
  ipv4_ipam_pool_id   = aws_vpc_ipam_pool.prod.id
  ipv4_netmask_length = 24

  tags = {
    Name        = "production-api-vpc"
    Environment = "production"
  }
}
When provisioning edge infrastructure, such as an aws ipam alb routing topology, IPAM reserves dedicated non-overlapping public and private subnets. Programmatic teams interact with the aws ipam api to trigger allocation checks during automated deployment workflows.
8. Automation vs Manual IPAM: Cost, Audit Trails, and Operational Scale
Comparing automation vs manual ipam reveals how manual IP address tracking introduces human error, configuration drift, and unmonitored exhaustion risks. Automated IPAM solutions provide programmatic API provisioning, real-time CloudWatch monitoring, and automated CIDR conflict prevention across cloud environments. While automated tools carry usage costs, they eliminate catastrophic cross-account routing outages.
Deciding between automation vs manual ipam involves balancing tooling overhead against outage risks. For large enterprises, establishing disciplined ipam automation strategies delivers verifiable operational savings:
| Governance Capability | Manual Tracking (Spreadsheet) | Automated AWS IPAM |
|---|---|---|
| Audit Trail Generation | No historical change audit trail | Native ipam audit trails in CloudTrail |
| Tag Governance | Unenforced metadata consistency | Automated ipam tag management rules |
| Observability & Alarms | Silent capacity exhaustion | Real-time ipam event logging via CloudWatch |
| Cost Profile | Zero software license fees | Usage-based hourly fee per managed IP |
Understanding aws ipam pricing and overall aws ipam cost structure ensures teams budget effectively. Comparing aws ipam free tier vs advanced tier options clarifies available governance: the Free Tier monitors public IPv4 addresses within a single account at zero cost, while the Advanced Tier monitors both public and private addresses across entire AWS Organizations for $0.00027 per active IP per hour. Implementing strict ipam cost control rules—such as excluding ephemeral test sandboxes from the IPAM scope—keeps cloud networking expenses predictable. For teams seeking aws ipam alternatives, self-hosted open-source tools like NetBox or commercial solutions like Infoblox provide hybrid data center coverage, while AWS IPAM delivers frictionless cloud-native integration.
Network architects must also evaluate known aws vpc ipam limitations. Currently, IPAM pools cannot span across multiple default private scopes within a single organization, and top-level supernets require upfront operational planning to accommodate hybrid ipam integration with clouds. For enterprise routing topologies, native aws ipam transit gateway integration ensures route propagation respects allocated pool boundaries without collision. Automating these definitions with terraform aws vpc ipam resource blocks (such as aws_vpc_ipam and aws_vpc_ipam_pool) guarantees consistent environment provisioning across infrastructure pipelines. To maintain cost efficiency across the rest of your AWS bill, consult our guide to reduce AWS costs without breaking production.
8. Subnetting Cheat Sheet for CCNA, Network+ & CKA Certification 2025 — Plus IPv6
Mastering subnetting remains mandatory across foundational infrastructure certifications including CCNA, CompTIA Network+, and Certified Kubernetes Administrator examinations. As enterprise networks scale into hybrid cloud topologies, engineers must also configure dual-stack IPv6 in VPC2025 environments. Understanding global unicast prefixes and EUI-64 addressing guarantees permanent immunity from IPv4 address depletion in modern production systems.
CCNA & Network+ Subnetting Exam Tips
Subnetting questions appear in every CCNA (200-301) and Network+ (N10-009) examination. Candidates relying on a quick-reference subnetting cheat sheet ccna format frequently ask how do i practice subnetting for ccna or network+ certification in 2025 and how do i practice subnetting for ccna or network certification in 2025. Candidates encounter three primary question patterns:
- Find Subnet Network and Broadcast: Given an IP and prefix, identify the boundary boundaries using the Magic Number method.
- Maximum Usable Hosts: Calculate available address space using
2^(32 − prefix) − 2(or minus 5 in AWS VPC scenarios). - Variable Length Subnet Masking (VLSM): Carve unequal subnets efficiently without wasting unallocated IP space.
CKA Exam Networking (Kubernetes Certified Administrator)
In the CKA exam, networking challenges focus on pod-to-pod communication, cluster CIDR routing, and CoreDNS resolution. Candidates must verify that host subnets do not collide with the cluster Pod CIDR or Service CIDR defined in kube-controller-manager manifests.
IPv6: The Long-Term Solution to IP Exhaustion
While prefix delegation and AWS IPAM optimize IPv4 allocation, deploying ipv6 in vpc2025 provides the long term solution to ip exhaustion. AWS provisions a /56 IPv6 CIDR block to your VPC, from which each subnet receives an immense /64 prefix containing 18.4 quintillion addresses.
- Every single pod in an EKS cluster receives a globally unique, routable IPv6 address.
- No NAT gateways required for outbound internet communication (managed via Egress-Only Internet Gateways).
- Zero CIDR overlaps between VPCs, spoke Transit Gateways, or on-premises networks.
9. Conclusion: Active Recall Beats Passive Documentation
Building high-performance cloud infrastructure requires transitioning from passive documentation reading to active problem-solving drills. Memorizing binary tables produces brittle understanding, whereas hands-on practice with mental math shortcuts, real-world failure postmortems, and automated IPAM architectures builds lasting engineering intuition. Mastering these core networking disciplines ensures resilient VPC deployments across enterprise platforms.
Senior platform engineers and cloud architects do not rely on static web calculators during live high-severity outages. Master the Magic Number formula, account for AWS's 5 reserved IP addresses, implement automated IPAM governance across multi-account clouds, and drill your reflexes with the free CIDR & Subnetting Speed Challenge.
Ready to Test Your Networking Speed?
Play the CIDR & Subnetting Speed Challenge: completely free, zero logins, zero tracking. Drop your highest Blitz score and streak in the comments!
🎮 Play Free at games.naveedkumbhar.com →When troubleshooting pod IP exhaustion and AWS VPC CNI subnet starvation during cluster autoscaling, consult our detailed incident breakdown in Kubernetes Real World Problems: 12 Production Postmortems.
For quick review before testing your speed, these frequently asked questions aws subnetting cidr 2025 address essential exam concepts and operational best practices.
To conduct a comprehensive review of your organization's cloud networking, explore our DevOps infrastructure audit playbook. For consulting inquiries or architectural advisory, review the About Naveed Ahmed overview or get in touch directly via Contact Naveed Ahmed.
Frequently Asked Questions
Direct answers to frequent engineering questions regarding AI coding agent disruptions, entry-level career outlooks, computer science degree value, and the changing landscape of software development roles in production environments.
What is AWS IPAM and when should I use it?
AWS IP Address Manager (IPAM) automatically tracks, audits, and allocates CIDR blocks across multi-account, multi-region AWS environments. Use it when managing more than five VPCs, multiple AWS accounts in AWS Organizations, or Transit Gateway hub-and-spoke architectures where overlapping CIDRs would break routing.
Why does AWS reserve 5 IP addresses per subnet instead of 2?
AWS reserves five IP addresses across every VPC subnet for infrastructure functions: the network identifier (.0), VPC router (.1), Amazon DNS resolver (.2), future capability reservation (.3), and network broadcast address (.255). Only n minus five addresses remain usable for EC2 instances or container pods.
How do I use this subnetting cheat sheet with the Magic Number method?
This subnetting cheat sheet uses the Magic Number method to calculate subnet boundaries instantly. Subtract the interesting octet mask value from two hundred fifty-six to find the block increment size. All subnet network addresses step in exact multiples of this number, allowing instant calculation of broadcast and usable host ranges.
How does Kubernetes Pod CIDR exhaustion happen on AWS EKS?
The AWS VPC CNI assigns real VPC subnet IPs directly to each Pod. An m5.2xlarge node can host up to 58 pods. A /26 subnet providing 59 usable IPs in AWS is fully exhausted by just two high-density worker nodes, causing new pods to fail with no free IP addresses available.
What is the minimum subnet size in AWS VPC?
AWS enforces a minimum VPC subnet size of /28. A /28 block contains sixteen total addresses, of which AWS reserves five, leaving only eleven usable IPs. For production Amazon EKS worker nodes and containerized workloads, platform engineers should provision /24 or larger subnets.
How do I practice subnetting for CCNA or Network+ certification in 2025?
Practice with timed repetition drills using the Magic Number method. The free CIDR and Subnetting Speed Challenge provides a 60-second Speed Blitz, 10-question Precision Sprint, and 32-bit Binary Flipper that directly map to CCNA 200-301 and CompTIA Network+ N10-009 exam question formats.
What AWS IPAM does and how does it prevent CIDR overlaps?
What AWS IPAM does is centralize address management across multi-account AWS Organizations. It automates CIDR provisioning from hierarchical pools, monitors utilization thresholds in real time, logs compliance audit trails, and actively prevents overlapping subnet allocations that break Transit Gateway routing tables.